

A response plan that nobody has tested is paperwork, not readiness. For an MSP, incident response plans work only when everyone knows who leads, who escalates, and what happens next. During a real incident, unclear ownership between your team, the client, and outside responders can delay decisions when time matters.
A document alone won’t create coordination. You need a practical operating playbook: clear enough to use under pressure, flexible enough to fit each client, and tested before an incident exposes gaps. This guide offers a reusable template to clarify roles and actions, adapt the plan to each client’s environment, and support faster, more informed decisions.
You’ll also learn how to run tabletop exercises, capture lessons, and keep the plan accessible and current. We’ll cover decision points, outside responders, and how security visibility and client reporting can support coordination. You’ll see where expert-led incident response support may fit, too. The goal is less confusion, tighter coordination, and a more controlled path to recovery.
Key Takeaways
- Separate the response plan from security policies and technical runbooks so decision-makers can quickly find the actions and authority they need.
- Use a flexible response lifecycle that guides teams from preparation through recovery and allows them to revisit steps as new facts emerge.
- Make incident response plans usable across clients by documenting scope, severity levels, roles, contacts, and escalation paths.
- Set decision prompts for containment, client notification, evidence preservation, and recovery before an incident puts the team under pressure.
- Build a repeatable improvement cycle: review changes, exercise the plan, assign fixes, and confirm they’re complete.
What an incident response plan does for an MSP and its clients
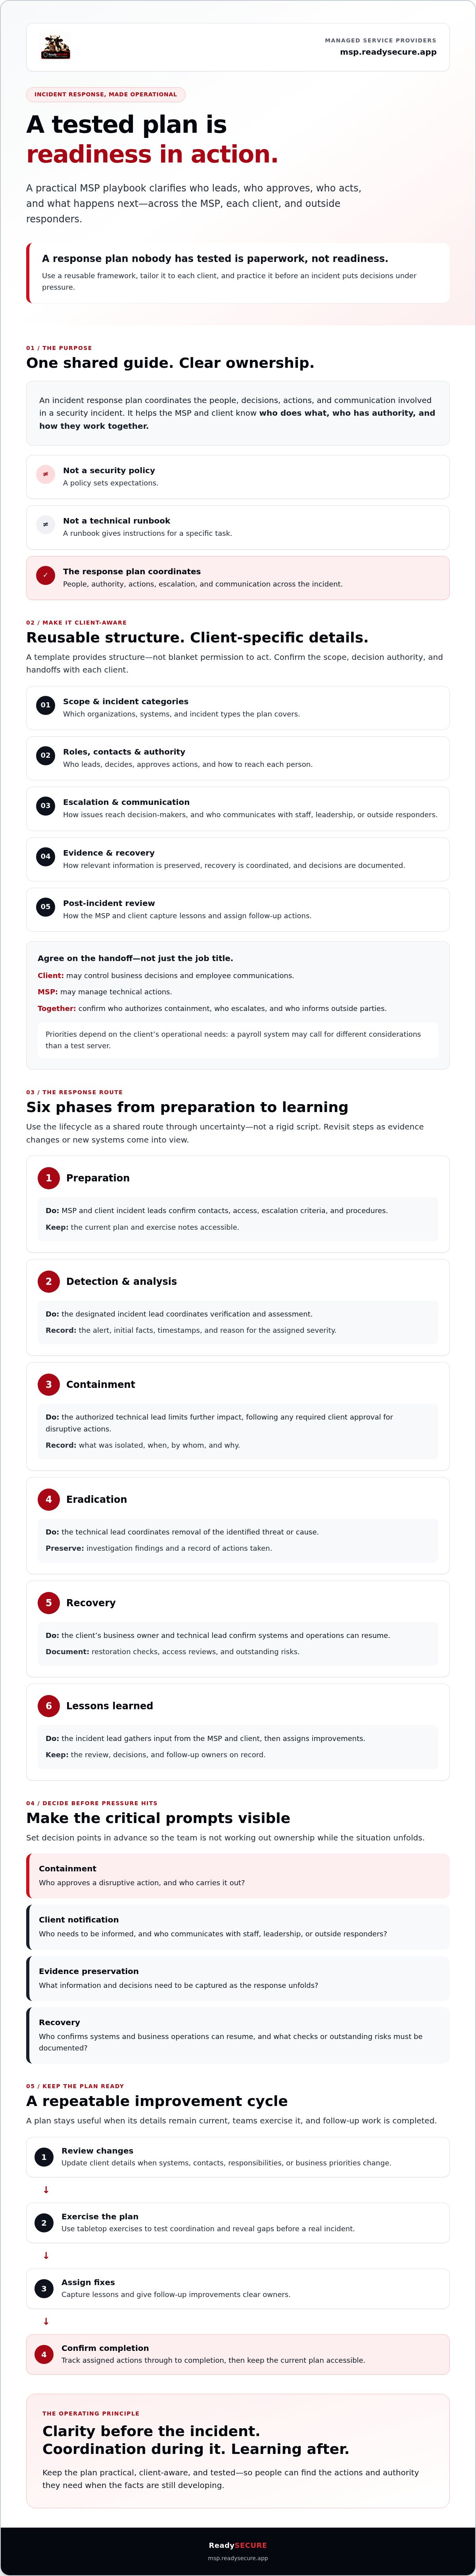
An incident response plan is a shared operating guide for making decisions, assigning actions, and communicating during a security incident. A security policy sets expectations, while a technical runbook gives instructions for a specific task. The response plan coordinates the people and decisions involved across the incident.
An incident response plan tells the MSP and client who does what, who has authority, and how they’ll work together when an incident occurs. For example, if a suspected account compromise calls for disabling access, the plan should identify who approves the action, who carries it out, and who needs to be informed. Without that clarity, teams may lose time determining ownership while the situation unfolds.
What belongs in an incident response plan?
Keep the core framework reusable, then record client-specific details in clearly marked fields. The plan should cover:
- Scope and incident categories: Which organizations, systems, and incident types the plan covers.
- Roles, contacts, and authority: Who leads, who makes decisions, who can approve actions, and how to reach each person.
- Escalation and communication: How issues reach the right decision-makers, and who communicates with staff, leadership, or outside responders.
- Evidence and recovery: How to preserve relevant information, coordinate recovery actions, and document decisions.
- Post-incident review: How the MSP and client capture lessons and assign follow-up actions.
Keep general response principles stable, but update client details when systems, contacts, responsibilities, or business priorities change. The plan should connect to the wider incident response lifecycle, from preparation through recovery and lessons learned, while giving teams practical instructions for their environment.
Why does an MSP need a client-aware response plan?
MSPs and clients share responsibility, but they may not share the same assumptions. The client may control business decisions and employee communications, while the MSP may manage technical actions. If neither side knows who can authorize containment or notify outside parties, a handoff can stall.
Context shapes the response. A system that supports payroll may need different priorities from a test server. The client’s operational needs, key systems, and decision-makers all affect which actions make sense and who must approve them. A reusable template provides structure, not blanket permission to act.
Before an incident, confirm each client’s scope, contacts, escalation paths, and decision authority. Document approvals clearly and make sure both sides can access the current plan. This turns a general framework into a working agreement the MSP and client can use together.
The incident response lifecycle: from preparation to recovery
Use the response lifecycle as a working sequence, not a rigid script. Teams may need to revisit earlier steps as evidence changes or new systems come into view. The lifecycle gives responders a shared route through uncertainty while leaving room to adjust as the facts develop.
For each phase, identify a decision owner, an essential action, and a record to preserve. Adapt these responsibilities to the client’s environment and agreed authority:
- Preparation: The MSP and client incident leads confirm contacts, access, escalation criteria, and response procedures. Keep the current plan and exercise notes accessible.
- Detection and analysis: The designated incident lead coordinates verification and assessment. Capture the alert, initial facts, timestamps, and reason for the assigned severity.
- Containment: The authorized technical lead limits further impact, following any required client approval for disruptive actions. Record what was isolated, when, by whom, and why.
- Eradication: The technical lead coordinates removal of the identified threat or cause. Preserve investigation findings and a record of actions taken.
- Recovery: The client’s business owner and technical lead confirm that systems and operations can resume. Document restoration checks, access reviews, and outstanding risks.
- Lessons learned: The incident lead gathers input from the MSP and client, then assigns improvements. Keep the review, decisions, and follow-up owners on record.
NIST finalized SP 800-61 Revision 3 in April 2025, superseding Revision 2. The linked NIST Computer Security Incident Handling Guide remains a reference for incident-handling practices. Use current guidance when developing procedures. For MSPs, incident response plans should make each phase understandable to both technical teams and client decision-makers.
What should the team do first after detecting an incident?
Verify the alert and capture initial facts, but don’t let investigation delay an urgent protective action. Apply the agreed escalation criteria, notify the incident lead and relevant client contacts, and start a shared incident record. Log timestamps, observations, decisions, and actions as they happen. These records support handoffs and help teams distinguish confirmed facts from assumptions.
How should containment and recovery decisions be handled?
Document who can isolate accounts, devices, or services, and who must approve actions that could disrupt business. Set recovery checks for restored systems, user access, backups, and essential operations. If a decision raises technical uncertainty or potential legal or regulatory duties, route it to qualified reviewers rather than making assumptions under pressure.
To pair documented workflows with security visibility, MSPs can explore ReadySECURE’s multi-tenant security platform. It can support service delivery, but it doesn’t replace client-specific response decisions or the plan itself.
Incident response plan misconceptions MSPs should address
Backups, security tools, and cyber insurance can support incident readiness, but none replaces a response plan. A tool may surface an alert and a backup may help restore data, but neither assigns decision authority, sets escalation paths, or coordinates communication between an MSP and its client.
A written document isn’t readiness by itself, either. If contact details are stale, staff have changed, or nobody knows who can approve a disruptive action, the procedure may fail when people need it. Keep ownership and approval paths current, then test whether the people named in the plan can use it under pressure.
Planning improves coordination, but it can’t promise that an incident won’t happen or guarantee a particular recovery outcome. Treat the plan as a framework for better-informed decisions, not a guarantee. NIST’s earlier Computer Security Incident Handling Guide offers foundational guidance. NIST finalized Revision 3 in April 2025, superseding Revision 2.
Does having backups mean an organization is ready?
No. Backups support recovery, but they don’t determine which systems to restore first, who approves restoration, or who communicates the impact to staff and leadership. Build those decisions into the plan. Identify business-critical systems, confirm who can access backup resources, and document how the team will verify backup availability and restoration integrity. Recovery priorities depend on the incident and the client’s environment, so avoid promising a universal recovery timeline.
Why do tabletop exercises matter?
A tabletop exercise is a guided discussion where the MSP and client work through a realistic incident scenario without making live system changes. It helps reveal whether the written plan holds up in practice.
For example, present a suspected compromised account and ask the group to explain how they would:
- Escalate the alert and reach the right decision-makers.
- Decide who can disable access and whether client approval is needed.
- Share updates internally and coordinate the MSP-client handoff.
- Record key decisions, actions, and unresolved questions.
After the discussion, turn each gap into a specific action, assign an owner, and set a review date. Update the plan when contacts, responsibilities, or procedures change, then confirm assigned fixes are complete. That’s the difference between keeping incident response plans on file and building a process people can follow.
Build an incident response plan template your MSP can adapt
Build one operating framework, then attach a client-specific annex. This keeps core procedures consistent across your service while capturing the systems, approvals, and priorities that differ by organization. Use the outline below to create incident response plans people can act on, not just file away.
Which template fields should every MSP complete?
- Plan scope: Client name, covered locations, systems, services, and incident categories.
- Severity and escalation: Severity levels, escalation triggers, and who must be notified at each level.
- Roles and contacts: MSP incident lead, technical responders, client decision-maker, alternates, and approved contact methods.
- Critical services and dependencies: Business priorities, key systems, third-party providers, and agreed communication channels.
- Decision prompts: Who approves isolating an account, device, or service? Who notifies the client, staff, or outside parties? How will evidence be preserved? Who approves restoration?
- Records and evidence: Instructions for capturing timestamps, decisions, and actions, plus the approved secure location for incident records.
Keep MSP-wide procedures, such as intake, escalation, and recordkeeping, in the core plan. Put environment-specific details in a separate client annex. This makes updates easier without blurring who owns each decision.
How should MSPs customize the plan for each client?
Map the client’s critical systems to its business priorities. Note service dependencies, relevant third parties, business hours, and operational constraints that could affect response. Then agree who can authorize service isolation, external notifications, and restoration decisions. Don’t assume the client’s most important system is obvious to the MSP. Confirm priorities with the people responsible for the business.
Validate contacts and approval paths during onboarding and scheduled reviews. Record primary and alternate contacts, the channels teams should use, and what to do if a decision-maker can’t be reached. Mark unresolved items rather than leaving blank fields that look complete.
Before adopting the template, check that it includes:
- A defined scope, system list, and severity criteria.
- Named role owners, alternates, and working contact details.
- Escalation triggers and approved communication channels.
- Clear approval prompts for containment, notification, evidence handling, and recovery.
- A secure record location and a client-specific annex with current details.
Use the checklist to spot gaps, then confirm decisions with the client before treating the plan as ready. For additional security support in your MSP service delivery, explore ReadySECURE for MSPs.
Test, maintain, and strengthen your incident response plan
A plan stays useful only if it keeps pace with the people, systems, and services it covers. Build a repeatable improvement cycle: review changes, exercise the plan, assign fixes, and confirm each fix is complete. Review contacts and procedures after major client or service changes, such as a new critical system, a change in MSP responsibilities, or updated escalation arrangements. Schedule reviews as well, so updates don’t depend on someone remembering.
How can an MSP validate its plan without disrupting operations?
Start with a discussion-based exercise. Use an illustrative scenario, such as a suspected compromised account, and ask the MSP and client to talk through escalation, decision authority, communications, and handoffs. The scenario is a practice tool, not a prediction. Record unclear ownership, missing information, and steps participants can’t explain. Assign every gap an owner and a review date, then check that it’s been addressed.
How should exercise findings and incident records improve the plan?
Use exercise notes and incident records to identify where procedures, contacts, or approvals need clarification. Keep updates controlled: document what changed, who approved it, and which client materials need revision. Then share the current version with the people expected to use it. If reviewing white-label delivery options is relevant to your MSP, see this guide to white-label security platforms for MSPs.
When should an MSP bring in incident response specialists?
Consider specialist support when investigation or recovery exceeds the capabilities your team and client have agreed on. ReadySECURE provides expert-led incident response support to MSPs and their clients. Before naming a provider in your plan, confirm its scope, engagement process, and availability directly. Define when to involve specialists and who makes that call, but don’t treat outside support as a substitute for client-specific roles or procedures.
What is the next step after the first plan is drafted?
Assign owners to open gaps and set a review date with the client. Document relevant security visibility and control context alongside the response procedures, so responders can work from a clearer picture of the environment. Keep incident response plans current, accessible, and part of a regular improvement cycle. To review security capabilities that may support your MSP’s service delivery, explore ReadySECURE’s MSP security capabilities.
Turn the plan into a stronger MSP service
A practical response plan does more than document procedures. It gives your team and each client clear roles, decision paths, and next steps across the incident lifecycle. Keep the framework reusable, tailor the details to each client, and exercise it to uncover gaps before pressure tests the process.
Make incident response plans part of an ongoing operating cycle: review changes, practice decisions, assign fixes, and confirm they’re complete. That discipline helps your MSP and clients coordinate with greater clarity, without promising that a plan can prevent every incident or guarantee recovery.
ReadySECURE can complement that work with expert-led incident response support for MSPs and their clients. Its multi-tenant platform brings together multiple security capabilities to support MSP service delivery. These resources can strengthen your approach, but they don’t replace a client-specific plan.
Explore ReadySECURE security capabilities for MSPs, and keep building a response process your team and clients can put into action with confidence.
Frequently Asked Questions
What is an incident response plan?
An incident response plan is an operating guide that explains how an organization and its service providers coordinate decisions and actions during a security incident. It identifies who leads, who has authority, how teams escalate issues, and how they communicate. Unlike a security policy or technical runbook, it connects people and procedures across the response. The plan should fit the client’s environment and remain accessible to everyone with a response role.
What should an incident response plan include?
Include the plan’s scope, incident categories, severity criteria, roles, contacts, escalation paths, and decision authority. Add instructions for communication, evidence handling, containment, recovery, and post-incident review. Specify which actions require client approval, where to keep incident records, and how to involve outside responders. Keep reusable procedures separate from client-specific details, such as critical systems and contact information, so those details can be updated without rebuilding the entire plan.
How do MSPs create an incident response plan for clients?
MSPs can start with a common framework, then customize it for each client. Identify critical systems, business priorities, third-party dependencies, and the people who can approve disruptive actions or notifications. Agree on escalation triggers, communication channels, and technical responsibilities. Validate the contact list and decision paths with the client, document unresolved gaps, and exercise the plan together. A template speeds up the work, but client approval makes it operational.
How often should an incident response plan be tested?
Set a recurring review and exercise schedule with each client, then test again after major changes to systems, contacts, responsibilities, or services. A discussion-based tabletop exercise can check whether participants understand escalation, decision authority, communications, and handoffs without changing live systems. Record what was unclear, assign an owner to each fix, and track completion. The right cadence depends on the client’s environment and changes, so don’t rely on a one-time test.
Does an incident response plan guarantee that a business can recover from ransomware?
No. A plan cannot guarantee recovery or prevent ransomware from disrupting operations. It can help teams coordinate decisions, preserve relevant evidence, communicate, and work through containment and recovery steps. Recovery also depends on the incident, affected systems, available backups, and the client’s environment. Document restoration priorities and verify backup access in advance. Define who approves recovery actions, then review progress against agreed checks rather than assuming a fixed recovery timeline.
What is the difference between an incident response plan and a disaster recovery plan?
An incident response plan coordinates how people identify, assess, and manage a security incident, including escalation, decisions, communications, and evidence handling. A disaster recovery plan focuses on restoring technology and business services after disruption. They support related but distinct needs. For example, an incident response plan may set out who authorizes isolating a compromised system, while disaster recovery procedures guide how the organization restores an affected service. Keep the plans aligned and clarify where responsibilities meet.
Can a small MSP manage incident response without dedicated security staff?
Yes, if the MSP defines its response responsibilities and limits before an incident. Name an incident lead, document escalation and client approval paths, and identify when investigation or recovery exceeds the team’s agreed capabilities. MSPs can also arrange qualified external support in advance. ReadySECURE provides expert-led incident response support to MSPs and their clients. Confirm scope and engagement arrangements directly, and don’t treat external support as a replacement for client-specific plans.


