

A place name in a ransomware list isn’t proof that a Newport Beach organization suffered a confirmed breach. That distinction matters when researching newport beach cyber incidents ransomware data breach 2025 2026: a June 2026 list names Newport Beach, but doesn’t identify an affected organization, confirm an incident date, or establish that data was exposed.
Search results can mix Newport Beach with wider Orange County events, while brief listings leave key facts unresolved. Treating every cyber event as ransomware can turn an unverified mention into a misleading conclusion.
This case study separates documented Newport Beach incidents from nearby reports and claims that lack confirmation. It explains what public evidence does and doesn’t establish, then draws practical lessons for prevention, response, and recovery. It also shows how local organizations and their managed service providers can improve security visibility, prioritize vulnerabilities, and plan incident response. The goal is to understand the evidence first, then use it to make better security decisions.
Key Takeaways
- Assess newport beach cyber incidents ransomware data breach 2025 2026 reports by checking the location, affected organization, incident date, and evidence of data exposure.
- Separate Newport Beach cases from broader Orange County events and reports about organizations that merely serve the area.
- Use incident records to identify unanswered questions, not to assume every cyber event involved ransomware or confirmed data theft.
- Strengthen your security baseline with asset visibility, prioritized vulnerability remediation, identity protections, email controls, and tested backups.
- MSPs can coordinate security work across clients by consolidating visibility into vulnerabilities, Microsoft 365 security, and mail security.
Newport Beach cyber incidents in 2025 and 2026: what counts as local and confirmed?
If you searched for newport beach cyber incidents ransomware data breach 2025 2026, the first step is to distinguish a documented local case from a regional mention. An organization headquartered in Newport Beach, an Orange County organization elsewhere, and a company that serves Newport Beach are not interchangeable. This case study counts an incident as local only when reliable reporting connects the affected organization or event to Newport Beach.
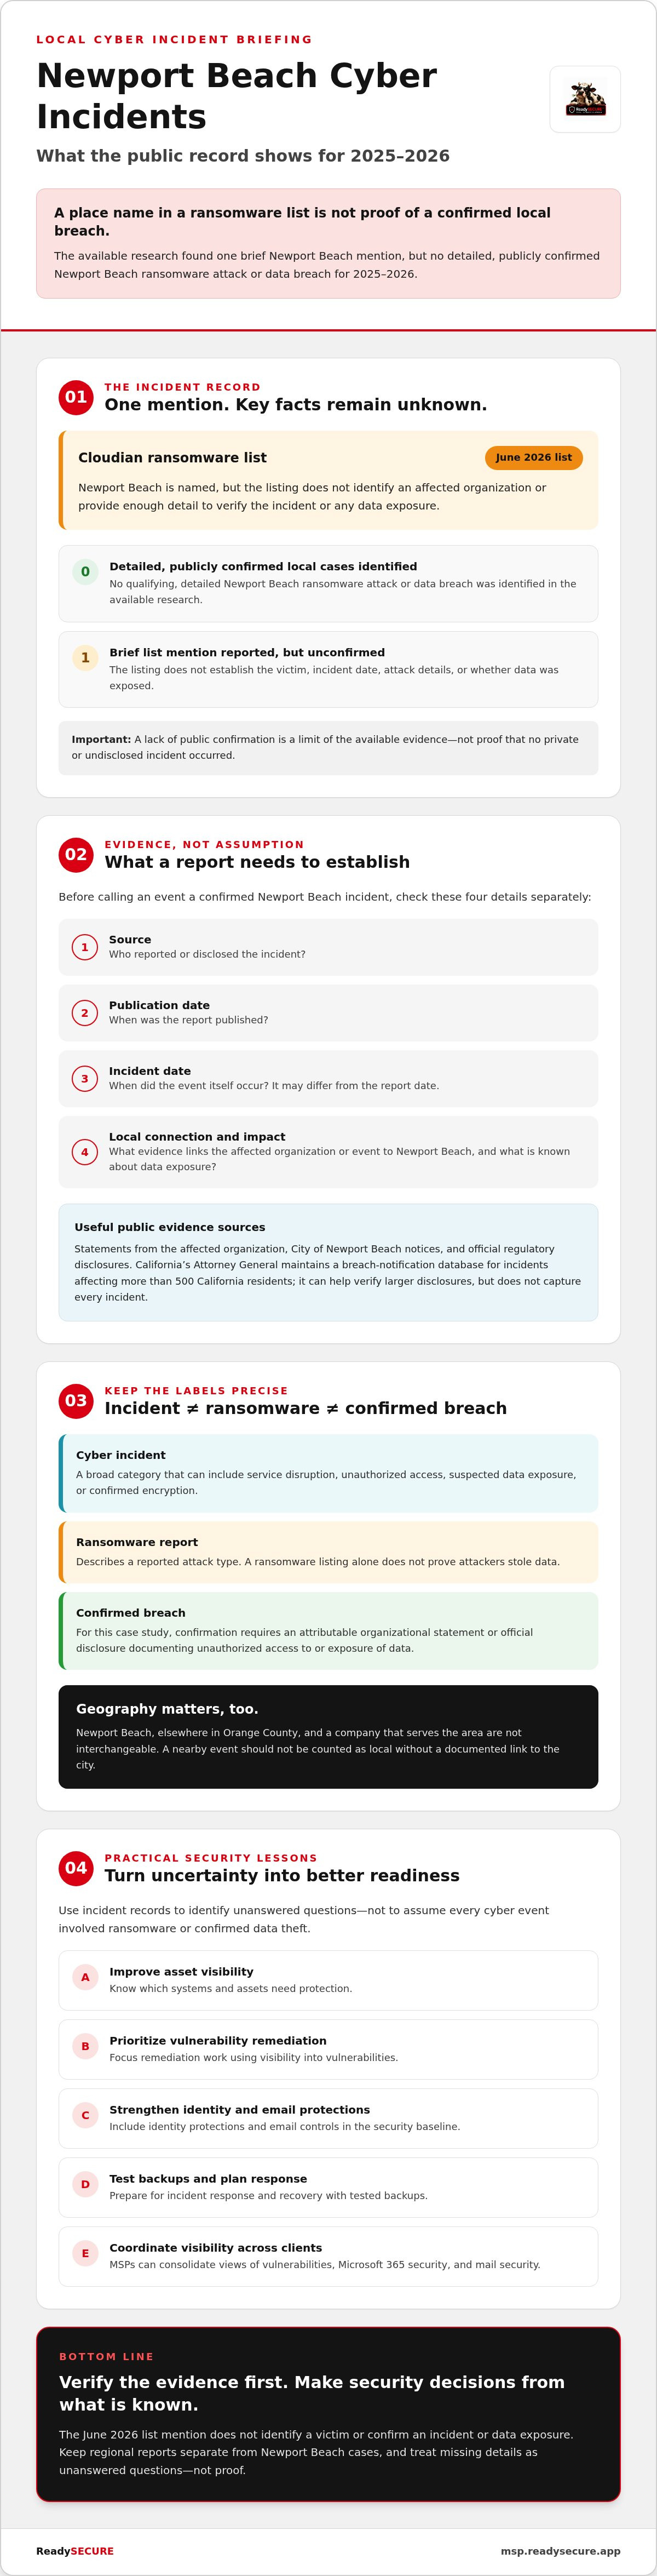
The public record identified for this period includes one brief Newport Beach mention in a list of ransomware attacks from June 2026, published by Cloudian. The listing doesn’t identify an affected organization or provide enough detail to confirm what happened or whether data was exposed. The available research identified no detailed, publicly confirmed Newport Beach ransomware attack or data breach. That is a limit of public evidence, not proof that no private or undisclosed incident occurred.
Incident status summary
- Confirmed: No qualifying, detailed public Newport Beach incident identified in the available research.
- Reported but unconfirmed: A June 2026 Cloudian list mentions Newport Beach, without sufficient details to verify the victim, incident, or data exposure.
- No verified public record: No additional Newport Beach-specific 2025 to 2026 case was identified. Nearby Orange County reports don’t count without evidence linking them to the city.
How to verify whether a cyber incident affected Newport Beach
Start with statements from the affected organization, City of Newport Beach notices, and official regulatory disclosures. California’s Attorney General maintains a public breach-notification database for incidents affecting more than 500 California residents. It can help verify larger disclosures, but it won’t capture every incident.
Track four details separately: the source, its publication date, the incident date, and the evidence connecting the event to Newport Beach. A report published in 2026 may describe an earlier incident. Likewise, a local service provider’s involvement doesn’t establish that the provider itself was affected. Don’t classify an Orange County event as a Newport Beach case without a documented geographic link.
Ransomware, data breach, and cyber incident are not interchangeable
A cyber incident is a broad category. It can involve service disruption, unauthorized access, suspected data exposure, or confirmed encryption. Ransomware describes a reported attack type, not automatic proof that attackers stole data. For background on what ransomware is, see the overview of its common forms and history.
For this case study, a breach is confirmed only when an attributable organizational statement or official disclosure documents unauthorized access to or exposure of data. A ransomware listing alone doesn’t meet that evidence standard. Precise labels make the findings more useful.
What the 2025 to 2026 Newport Beach incident record actually shows
The evidence supports a narrow conclusion, not a full local incident timeline. The research identified one Newport Beach mention in a Cloudian list of ransomware attacks from June 2026. It didn’t identify an affected organization, establish when an attack occurred, or confirm encryption, data theft, or service disruption. The available research identified no detailed, publicly confirmed Newport Beach ransomware attack or data breach from 2025 to 2026.
| Date | Affected entity | Location evidence | Incident type | Source | Confirmation status |
|---|---|---|---|---|---|
| Incident date: unknown. List period: June 2026. Disclosure date: unknown. | Unknown | Newport Beach is named, but no organization or local connection is specified. | Ransomware listing; attack details and impact unknown. | Cloudian, 2026 list | Reported, but unconfirmed as a Newport Beach incident. |
| 2025 to 2026: no verified incident date identified. | No qualifying affected entity identified. | No additional Newport Beach-specific evidence identified in the research. | No additional confirmed incident type. | Available research; California Attorney General disclosures are a relevant source for qualifying breach notices. | No verified public record identified. |
Build a source-checked timeline without overstating the evidence
For a stronger record, prioritize statements from the affected organization, California Attorney General breach disclosures, and relevant agency records. Record the incident date separately from the date a notice or news report appeared. If dates or the victim’s identity are missing, mark them unknown rather than filling gaps with guesses.
FBI IC3 and CISA reports can explain broader ransomware patterns and response guidance, but they don’t prove a Newport Beach victim was affected. CISA’s ransomware prevention and response best practices can inform preparation, but they aren’t evidence for a local case.
What public reporting can and cannot establish
A ransomware group’s claim isn’t the same as an organization confirming unauthorized access or data exposure. An investigation may also be ongoing, leaving the scope or impact unresolved. State what the source confirms, attribute allegations clearly, and don’t estimate affected people, financial losses, or downtime without supporting evidence.
For the newport beach cyber incidents ransomware data breach 2025 2026 record, the June list entry remains a lead, not a verified case. A named victim, attributable disclosure, and confirmed impact would be needed to change that status. MSPs looking to organize security visibility across client environments can review the MSP security platform.
What verified ransomware or breach cases reveal about local business risk
A case study should distinguish what the evidence shows from what it leaves unanswered. For the newport beach cyber incidents ransomware data breach 2025 2026 record, the available research doesn’t establish a named local victim or a confirmed incident sequence. There’s no reliable basis to describe how an attacker gained access, which systems were affected, how long services were disrupted, or how recovery unfolded.
Those gaps matter. Without an organization’s statement or credible reporting that documents operational impact, claims about lost revenue, exposed records, downtime, phishing, weak passwords, or unpatched software would be speculation. A ransomware label alone doesn’t reveal the attack path or prove data theft. The reported Newport Beach mention isn’t enough to draw case-specific conclusions.
Trace the incident sequence only as far as evidence allows
For a verified case, build a timeline from sourced milestones: discovery, containment, disclosure, and recovery. Record only what the organization or a reliable authority confirms. Here, those milestones remain unknown, so there’s no defensible sequence to map. CISA’s #StopRansomware Guide offers prevention and response guidance, but general recommendations shouldn’t be presented as evidence about this unverified local report.
This distinction protects decision-making. An observed attack path can support a case-specific lesson. General advice can still guide preparation, but it should be labeled as broader security guidance, not a finding about a Newport Beach organization.
Translate case evidence into practical risk questions
Local relevance depends on an organization’s operations, data, technology, and connections to suppliers or customers, not city limits alone. A business outside Newport Beach may support local organizations, while a local company may rely on systems and vendors across many locations. Use that exposure to guide a review without implying a local incident occurred.
For your own environment, ask practical questions and document the answers:
- Are identity controls, including protections for privileged accounts, reviewed and maintained?
- Are backups protected, and have recovery procedures been tested?
- Do email controls help address phishing and suspicious messages?
- Are vulnerabilities tracked, with remediation prioritized by risk?
No verified Newport Beach case in this record confirms a Microsoft 365 connection. For broader MSP-focused context, review M365 security hardening tools for MSPs, without treating that guidance as evidence about a local victim. The disciplined takeaway is to separate confirmed facts, undisclosed details, and general prevention steps. That makes the next security decision more useful and credible.
How Newport Beach organizations can turn incident lessons into action
The available public record doesn’t establish a detailed Newport Beach case to copy. Preparation still matters. Use the uncertainty around newport beach cyber incidents ransomware data breach 2025 2026 as a prompt to build a response process that your organization and MSP can execute together.
Prepare before an incident disrupts operations
Start with visibility. Keep an inventory of critical systems, administrator accounts, vendors, and data stores. Note who owns each system and which business functions depend on it. Then rank known vulnerabilities by risk and remediation priority, rather than treating every finding as equally urgent. Review identity protections and email controls as part of the same baseline.
Backups matter only if you can restore from them. Test restoration and document who can authorize recovery, which systems come first, and how to isolate affected systems if compromise is suspected. Put escalation contacts, backup owners, and decision authority in a written response plan. Keep it accessible if normal systems or communication channels aren’t available.
Coordinate the response across the business and its MSP
Agree in advance who investigates, preserves evidence, communicates with employees and customers, and approves recovery actions. During a suspected incident, record key observations and decisions, preserve relevant logs and other evidence, and coordinate containment with the people responsible for affected systems. Avoid wiping or rebuilding systems before response leads have considered evidence needs.
Use routine vulnerability management and security configuration reviews to reduce known exposure before an incident. Your organization and MSP should know how to reach one another, what information to share, and who has authority to make time-sensitive decisions. MSPs comparing ways to coordinate repeatable security work across client environments can consult the guide to white-label security platforms.
Include communication and legal review in the plan. Identify who will prepare internal updates and who will assess external communications. If a suspected incident may involve personal information, consult qualified legal counsel promptly about applicable notification duties, deadlines, and the facts needed to assess them. Requirements can depend on the circumstances, so don’t rely on a generic checklist as legal advice.
For MSPs seeking consolidated visibility across client environments, review security management for MSPs. The goal is practical: know what you have, who decides, and how you’ll respond.
How MSPs can turn Newport Beach incident awareness into stronger client protection
The Newport Beach record is a reason to improve evidence-led security work, not to build client policies around an unverified report. For MSPs, the practical step is to turn each credible threat or incident review into a repeatable cycle: assess exposure, assign owners, track remediation, and confirm follow-through.
Turn one incident review into repeatable client security work
Translate relevant lessons into client-specific reviews. Check each environment’s vulnerabilities, Microsoft 365 security configuration, and mail protections. Then document the risk, assign a remediation owner, set a follow-up date, and record whether the issue was resolved or accepted with a clear rationale. Don’t assume every client has the same systems, exposure, or business priorities.
Multi-tenant visibility can help MSPs organize these tasks across managed environments and identify work that needs attention. A white-label approach can help an MSP present security work under its own brand. Where platform workflows support reporting and compliance evidence, use them to organize records for review and governance. These are visibility and documentation aids, not proof that a client is secure or that an incident will be prevented.
Keep the workflow accountable:
- Record findings and the evidence behind each one.
- Name the person responsible for remediation and the person who verifies completion.
- Set a follow-up date and escalate overdue high-priority work.
- Review recurring issues across clients without assuming one client’s findings apply to another.
Security tools support the process. They don’t replace human judgment, client-specific risk decisions, or a practiced incident response plan.
When an MSP may need specialist support
An MSP may seek vCISO guidance when a client needs strategic security direction, risk prioritization, or help aligning security work with governance goals. Incident-response expertise may complement an existing team when a suspected compromise requires structured investigation, evidence handling, containment decisions, or recovery coordination. Define responsibilities before an incident, including who leads, who advises, and who approves business decisions.
Confirm scope and availability directly before making commitments to clients. Don’t imply that a platform alone provides incident-response coverage or that specialist support is automatically available on a particular schedule. For the newport beach cyber incidents ransomware data breach 2025 2026 topic, the durable MSP lesson is to make security work visible, assigned, and reviewable, whether or not a local report is fully substantiated.
MSPs looking to coordinate vulnerability management, Microsoft 365 security, mail security, and compliance work across client environments can explore ReadySECURE’s white-label, multi-tenant security platform. Review its capabilities against your operating model and confirm service scope directly.
Turn careful reporting into stronger security decisions
The clearest finding from newport beach cyber incidents ransomware data breach 2025 2026 is that a brief local mention isn’t the same as a confirmed breach. Verify the affected organization, location, incident date, and documented impact before drawing conclusions. When public details are missing, mark them unknown.
An evidence-first approach still points to practical action: improve visibility across systems, prioritize remediation, protect identities and email, and test recovery plans. For MSPs, consistent tracking across client environments can turn security reviews into assigned work with clear follow-up.
ReadySECURE brings vulnerability management, Microsoft 365 security, mail security, and compliance into one multi-tenant console. MSPs can also explore expert-led incident response and vCISO support as professional services, with scope confirmed directly. Explore how MSPs can strengthen and scale client security.
Reliable security starts with clear evidence, defined ownership, and steady execution. Build those habits now so your team can make its next decision with greater confidence.
Frequently Asked Questions
Were there any confirmed cyber incidents in Newport Beach in 2025 or 2026?
No detailed, publicly confirmed Newport Beach incident was identified in the available research through September 2026. For searches about newport beach cyber incidents ransomware data breach 2025 2026, one June 2026 Cloudian ransomware list mentions the city, but doesn’t name an affected organization or confirm an incident date or impact. That gap limits what can be verified publicly; it doesn’t prove no private or undisclosed incident occurred.
Was a Newport Beach business affected by ransomware in 2025 or 2026?
The available research doesn’t verify a Newport Beach business as a ransomware victim during 2025 or 2026. The June 2026 Cloudian list names Newport Beach, but provides no business name or incident details to establish that a local company was attacked. Without an attributable statement from the affected organization or reliable reporting identifying the victim and evidence, treat the mention as unconfirmed, not as proof of a local ransomware case.
What is the difference between a cyber incident and a data breach?
A cyber incident is a broad event involving computer systems, such as disruption, suspicious access, or malware activity. A data breach specifically involves unauthorized access to or exposure of information, supported by evidence such as an affected organization’s statement or an official disclosure. Ransomware is an attack type. It may involve encryption or service disruption, but the label alone doesn’t establish that attackers stole or exposed data.
How can I check whether a reported breach affected Newport Beach residents?
Look for a notice from the affected organization and search the California Attorney General’s public breach-notification database, which covers reported breaches affecting more than 500 California residents. Check the notice for the organization’s identity, affected data, and resident impact. Compare the incident date with the notice’s publication date, since they may differ. The database won’t capture every incident, so an absent listing isn’t conclusive proof that no breach occurred.
What should a Newport Beach business do after discovering a suspected ransomware attack?
Activate your incident response plan and contact the people responsible for IT and security, including your MSP or incident-response provider. Coordinate containment of affected systems, preserve relevant logs and evidence, and document key decisions before systems are rebuilt or wiped. Use a trusted communication channel if normal systems may be compromised. If personal information could be involved, consult qualified legal counsel promptly about applicable notification duties and deadlines.
Can an MSP help a business prepare for ransomware and data breaches?
Yes. An MSP can help review vulnerabilities, Microsoft 365 security, and mail protections, and coordinate security tasks and response planning with the business. ReadySECURE provides MSPs with a multi-tenant platform for vulnerability management, Microsoft 365 security, mail security, and compliance. It also offers vCISO support and incident response as professional services. Tools and preparation support a stronger process, but can’t guarantee that an incident will be prevented.
What should an incident report include before I treat it as confirmed?
Look for the affected organization’s name, a reliable source, the date the incident occurred, the date it was reported, and evidence connecting it to Newport Beach. The report should distinguish confirmed facts from attacker claims or details still under investigation. Check whether the organization or an official disclosure confirms unauthorized access, data exposure, encryption, or disruption. If key details are missing, label them unknown rather than treating the report as a verified case.


